Independent project / case study
CIS Mini RMM.
A Windows agent, a narrow gateway, and a control plane built to make endpoint administration more deliberate. Follow the path from first enrollment through a verified update.
Independent technical project
One agent. A complete control path.
A private endpoint-management project that connects Windows services, APIs, databases, network boundaries, and signed updates into one traceable workflow.
Enroll
One-time, high-entropy tokens are hashed at rest and expire when redeemed. Devices receive their own ID and secret.
Report
A Windows service phones home with heartbeats and version information through a restricted nginx gateway.
Recover
A separate Auditor watches the Agent and can restart it with retry and backoff behavior.
Update
Maintenance tooling checks signed release artifacts before replacing the installed Agent.
Interface preview
Inside CIS Mini RMM.
Working API Alpha Version 10.9.26 - Private use only
Platform architecture
Follow the signal.
Select a layer to see what it does and how data moves through the system.
Start with a known device.
A one-time enrollment token gives each device its own ID and secret. The Agent reports heartbeats and version information, while the separate Auditor watches for recovery and maintenance work.
- Device identity
- Outbound reporting
- Watchdog recovery
Keep the path narrow.
Endpoints initiate outbound communication through Cloudflare and a restricted nginx gateway. The agent route is separated from the broader administration surface.
- Outbound connection
- Restricted agent routes
- Public entry boundary
Turn reports into durable state.
The ASP.NET Core API handles device and organization records. PostgreSQL holds the data, migrations, and release catalogue that make health and update decisions traceable.
- Device and organization API
- PostgreSQL records
- Release metadata
Give technicians a clear view.
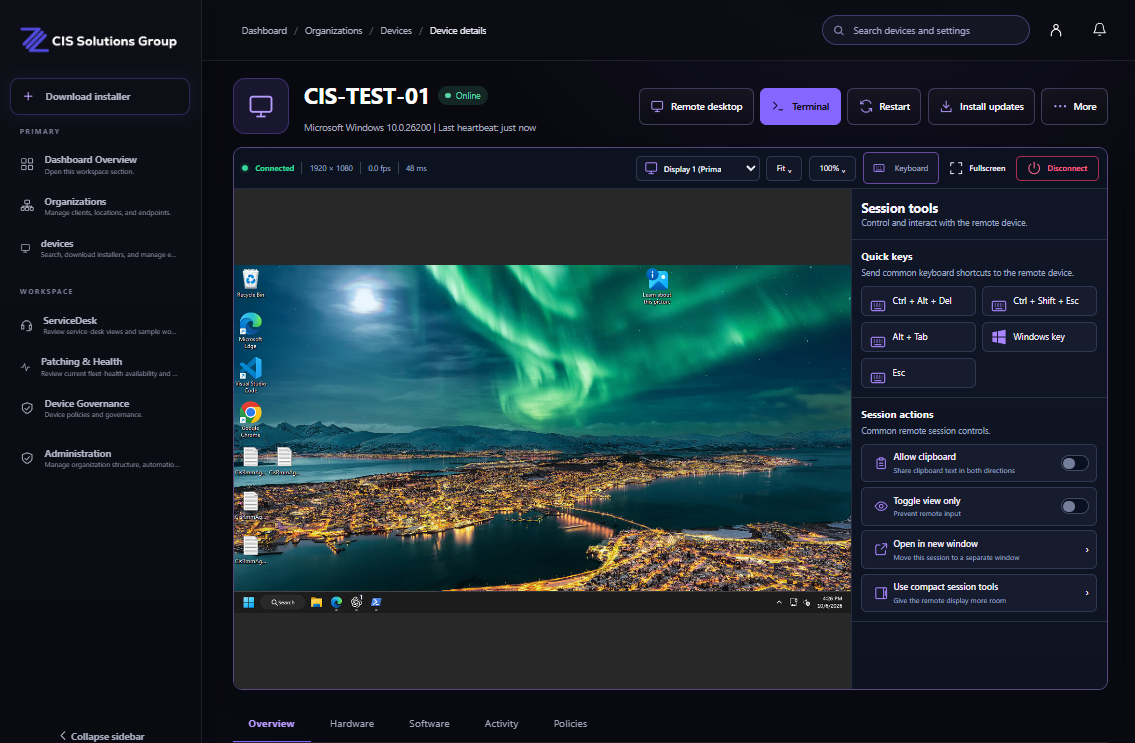
The Admin Center brings device health, versions, and management tools together. The remote session shown above is part of ongoing work; per-user authorization and the full browser workflow are still being developed.
- Device visibility
- Version tracking
- Remote tools in development
Security by design
Trust is a workflow.
Key decisions in the build include single-use enrollment, device identities, a dedicated agent gateway, outbound endpoint communication, and RSA-signed software releases. Self-update has been tested end to end with the new version reported back by the API.
Device lifecycle and remote control
The planned lifecycle covers pending, approved, active, suspended, rejected, decommissioned, and archived states. Tokenless bootstrap keeps unknown devices quarantined until approval. The Admin Center preview shows a remote session in development; per-user remote-control authorization and the complete browser workflow remain design work.
Remote terminal execution is currently in the SYSTEM context; interactive-user execution is being examined.
Release engineering
Update the endpoint with evidence.
The release flow is designed to verify both package integrity and publisher authenticity before installation.
A self-update test replaced an installed Agent and the API subsequently reported the new version.
Keep exploring